Webinar · Baseline IT × 7AI
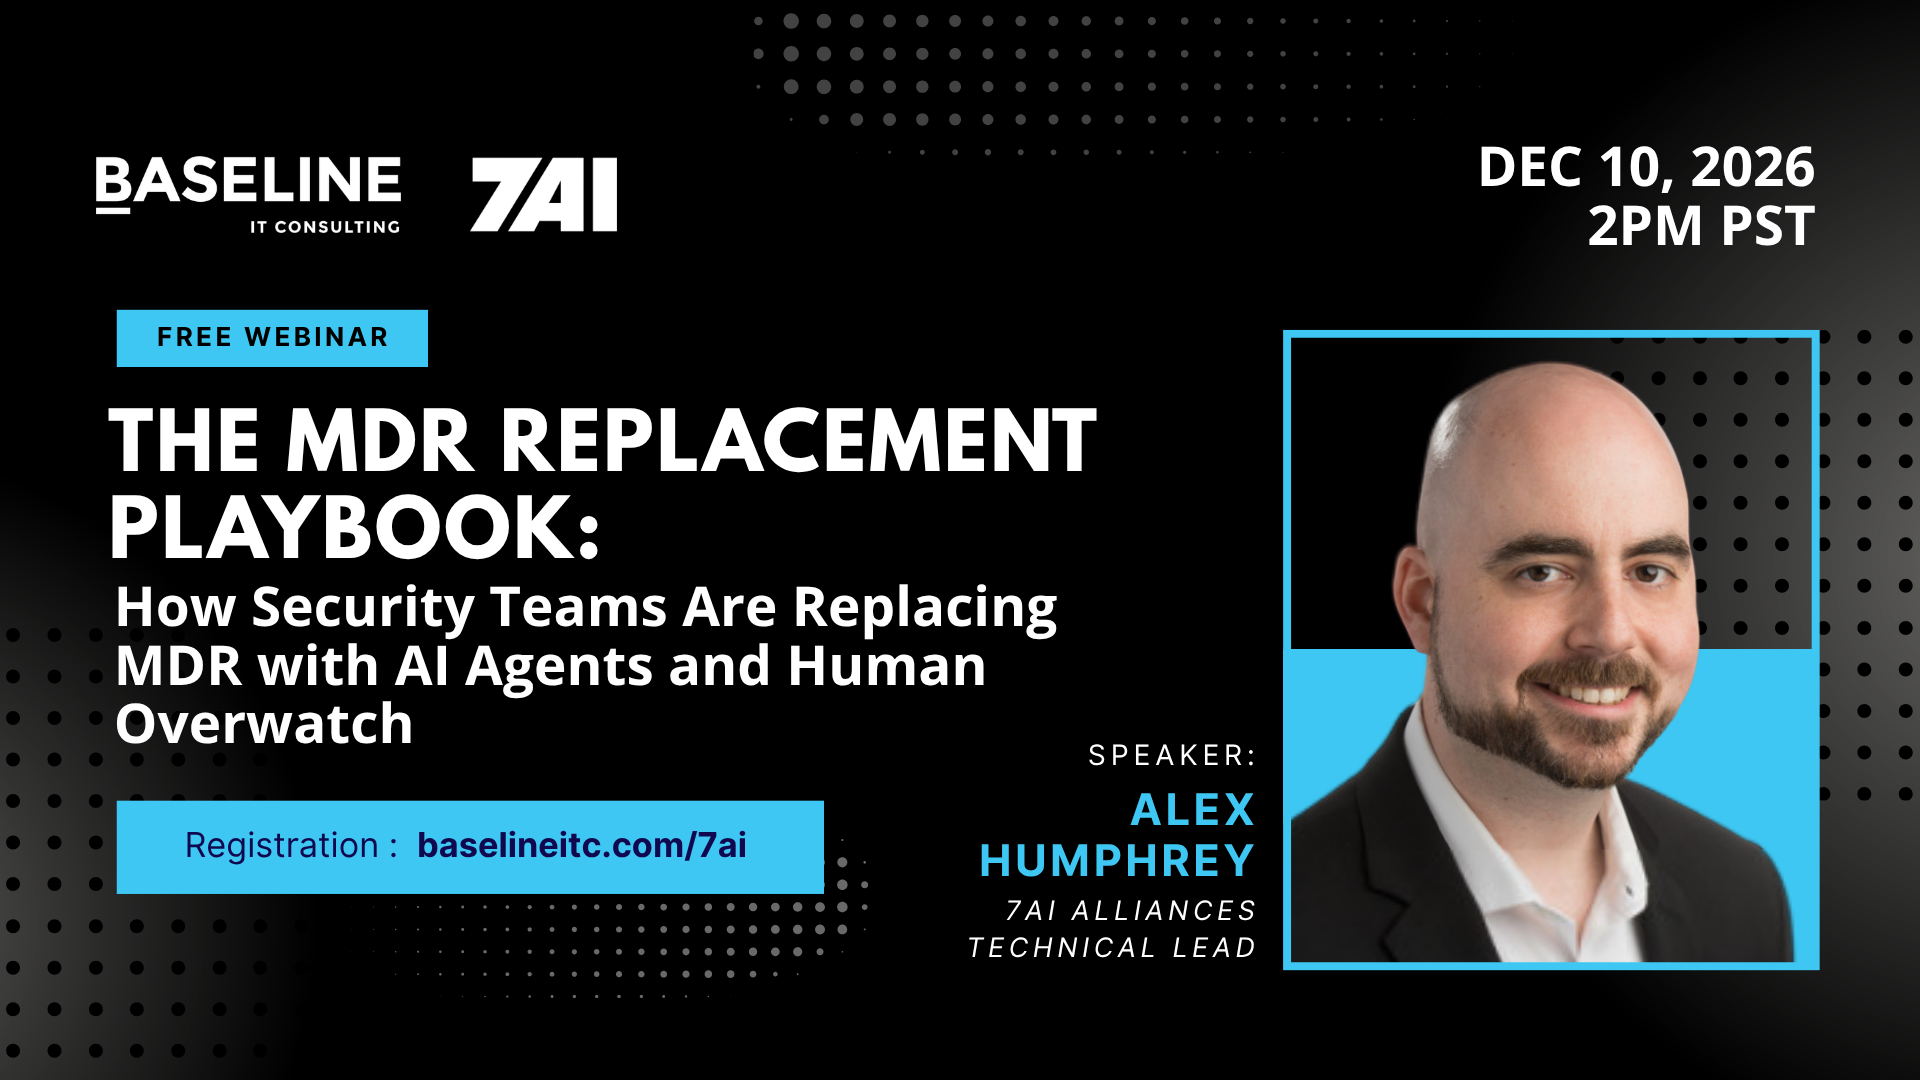
The MDR Replacement Playbook: How Security Teams Are Replacing MDR with AI Agents and Human Overwatch
Most security teams did not choose their MDR because they loved it. They chose it because 24x7 coverage was the only way to keep up, even if that meant slow escalations, no visibility into what was and was not investigated, and alerts that still landed on the internal team.
A growing group of security leaders has replaced that model. In this session, Alex Humphrey of 7AI walks through what they have in common: the problems that pushed them to look, how they evaluated an AI SOC against a traditional MDR, why they made the switch, and the results they are reporting now, including investigation times measured in minutes and escalation rates under 1%.
Then Alex shows the platform live: how AI agents investigate every alert end to end, how the PLAID ELITE team provides 24x7 overwatch, and what your analysts actually see.
For security and IT leaders evaluating their MDR renewal, or wondering what comes after it.
Date
Thursday, December 10, 2026
Time
2:00 – 3:00 PM PST
Format
Live virtual technical demo
Partner spotlight
About 7AI
7AI builds an agentic security platform that moves from detection to investigation and response across identity, cloud, email, endpoint, and SaaS. Its operating model is PLAID—People-Led, AI-Driven: AI agents perform the investigative work, while people retain judgment, strategy, and oversight. Rather than stopping at alert triage, 7AI describes a full investigation of every alert, with an explainable determination, linked evidence, and actionable remediation. Its Federated SIEM connects existing SIEMs and security data lakes, allowing detection, search, and enrichment across connected sources without requiring all logs to move into one store.
From alert to resolution
Collect the alert and its context
Agents retrieve the source data, enrich it with your environment’s context, and use connected security tools to investigate. Emails, domains, files, hashes, and users are linked in an artifact graph so analysts can trace relationships and check prevalence across the environment.
Reach an evidence-backed determination
Each investigation leads with a verdict, its reason, the supporting findings, and recommended actions. Analysts can inspect each agent’s mission, tools, exact requests and responses, and reasoning—not just accept an unexplained score. An investigation-specific copilot answers follow-up questions from the case’s own evidence.
Contain through the tools you already own
Response actions can revoke sessions, reset passwords, isolate hosts, block hashes, or quarantine malicious files. Approval gates keep people in control, while workflows automate repeatable steps with conditional logic. Actions are tied to the investigation and recorded in an audit trail.
Carry the case through resolution
Cases retain the verdict, priority, ownership, and status from open through closed. Workflows can trigger when an investigation completes or a case changes, while runbooks keep incident procedures alongside the work rather than in a separate document.
The managed SOC: PLAID ELITE
PLAID ELITE is the fully managed service built on that platform. A dedicated AI Security Engineer adapts it to the customer’s environment, and a 24×7 team oversees escalations and response. Routine containment follows a response policy approved in advance; decisions outside those boundaries reach the customer with root cause, timeline, evidence, and recommended actions. A named team retains environment-specific context, including exceptions, VIPs, and maintenance windows—so the handoff is a complete investigation, not another alert for your team to rebuild.
Product capabilities described by 7AI. Specific integrations and response permissions depend on the deployment.
Who should attend
West Coast security leaders and evaluators at organizations in the $500M–$1B segment with upcoming MDR renewals.
What you'll see
- See 7AI's agentic security platform investigate and respond to alerts in real time.
- Understand how 7AI's functions compare to traditional MDR providers.
- Get practical guidance to bring into your upcoming MDR renewal.
Registration opens soon
Want a seat saved? Reach out and we'll make sure you get the invite.
Contact us