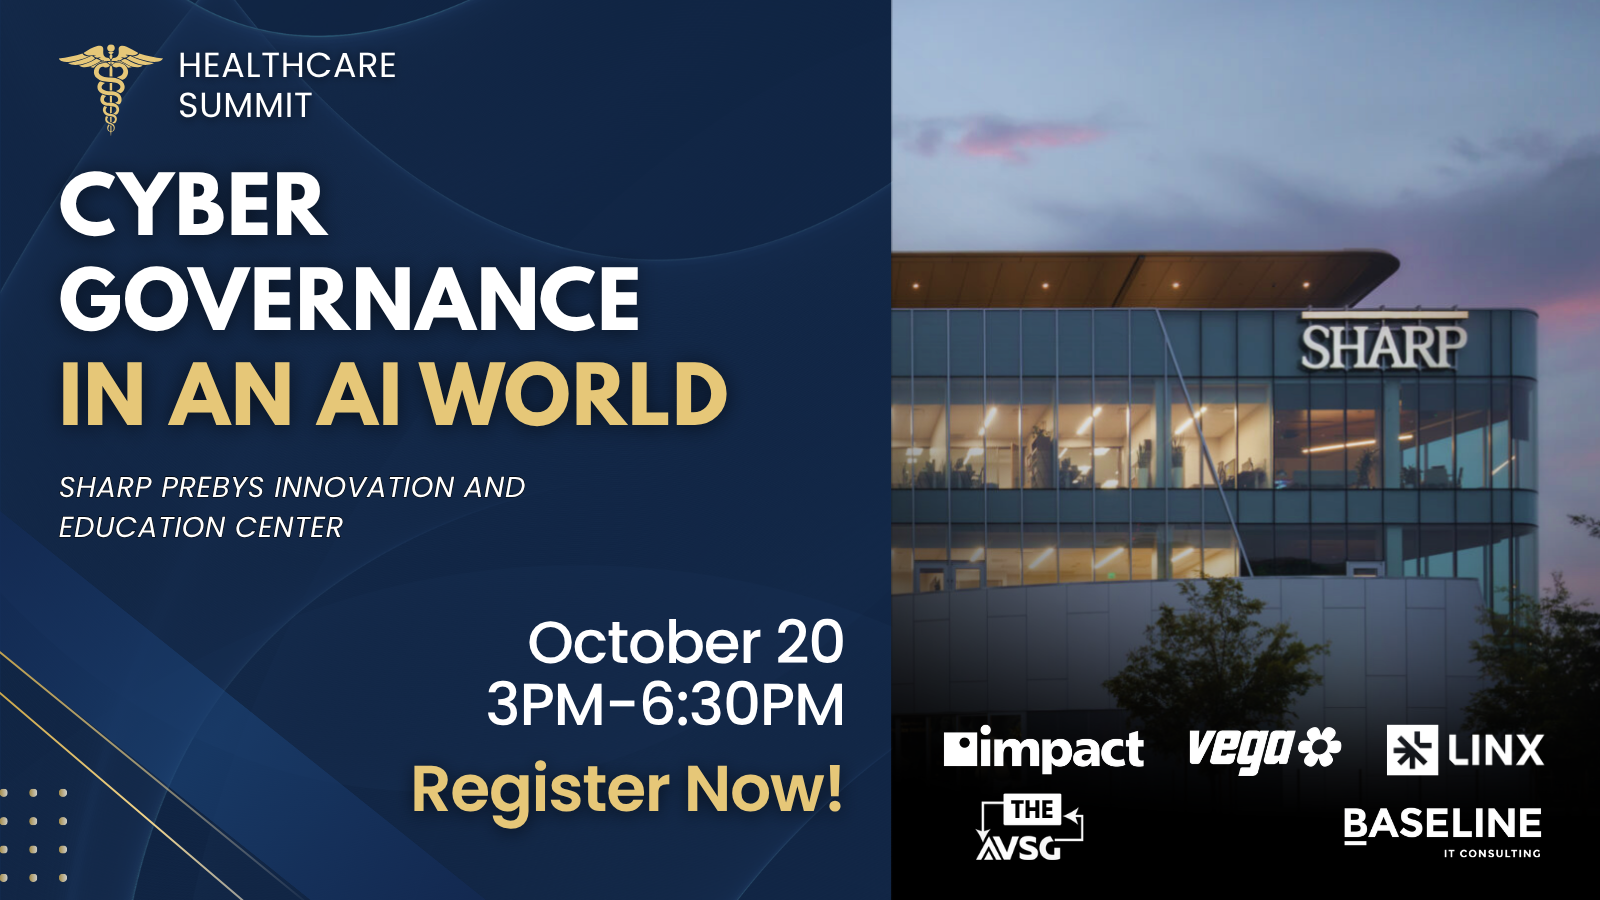
Healthcare Summit: Cyber Governance in an AI World at Sharp Prebys Innovation and Education Center, October 20, 3–6:30 PM — Register now

Healthcare Summit

Cyber Governance IN AN AI WORLD

SOC operations and identity security for AI in healthcare. 

Free to attend · Space is limited

Register on LinkedIn

Date

Tuesday, October 20, 2026

Time

3:00 PM – 6:30 PM

Venue

Sharp Prebys Innovation and Education Center, San Diego, CA

Hosted by

Baseline IT Consulting and The AVSG

Why this summit

The attack surface moved

As AI moves from pilot programs into daily clinical and administrative workflows, healthcare organizations face a widening attack surface — not just at the network perimeter, but at the level of every human and machine identity touching patient data.

This summit brings together healthcare IT, security, and compliance leaders for a focused look at two questions: how a modern Security Operations Center protects a healthcare environment, and why identity- and user-level controls are now the front line of AI security in healthcare.

Who should attend

  • Healthcare CISOs, CIOs, and IT security leaders
  • SOC managers and cybersecurity operations staff
  • Clinical informatics and digital health leaders evaluating AI tools
  • Compliance, privacy, and risk officers
  • Health system executives preparing AI governance policy

Agenda

The schedule for the day

Tuesday, October 20, 2026 · 3:00 – 6:30 PM
Sharp Prebys Innovation and Education Center, San Diego

3:00 – 3:30

Registration

3:30 – 3:50

Welcome & Opening Remarks

  • Ian Fasack — CEO, Baseline
  • Dennis Pappenfus — CEO, The AVSG

3:50 – 4:20

Governance Without Visibility Is Just Paperwork: Securing AI in Healthcare

4:20 – 4:50

Modern Identity Governance for the Modern Healthcare Enterprise

4:50 – 5:10

20-Minute Break

5:10 – 5:40

AI in Healthcare: The Security Conversation Nobody Scheduled

5:40 – 5:55

Closing Remarks

5:55 – 6:30

Networking Reception

3:50 – 4:20

Governance Without Visibility Is Just Paperwork: Securing AI in Healthcare

Tim Hankins · Vega

AI agents are now at work across healthcare, touching clinical, operational, and administrative data. Attackers run on the same frontier models and break in within minutes. Yet most security teams can’t see what their own agents actually do, and the legacy SIEM sees only what they can afford to ingest. The rest, spread across EHRs, cloud platforms, and connected devices, goes unmonitored.

Join Vega for a conversation on Agentic Cyber Defense: hunting, detection, and triage running as one agentic loop, right where your data lives, with AI agent activity covered like any other source. Drawing on Vega’s work with leading healthcare providers, we’ll share the core principles for governing AI: judge agents by their actions rather than their outputs, keep sensitive data under your control, and make every AI decision traceable to its evidence.

Bring your questions on AI governance, coverage gaps, and whether to augment or replace your legacy SIEM.
4:20 – 4:50

Modern Identity Governance for the Modern Healthcare Enterprise

Jeff Westphal · Linx Security

Healthcare organizations manage one of the most complex identity environments in the enterprise, spanning clinicians, employees, contractors, travel nurses, third parties, service accounts, and increasingly AI agents. As access changes across hospitals, applications, cloud environments, and legacy systems, traditional governance processes struggle to keep pace.

This session will explore how healthcare security teams can modernize identity governance with continuous visibility, automated lifecycle management, least privilege, and governance across human and non-human identities, reducing risk while making identity operations easier to manage.

5:10 – 5:40

AI in Healthcare: The Security Conversation Nobody Scheduled

Dr. Robert J. Becker · DOT Security

Healthcare is adopting AI faster than nearly any other industry, and attackers have taken notice. A patient record still sells for several times what a stolen credit card commands, and most of the AI now running in health systems arrived through a vendor update rather than a security review.

Dr. Robert Becker, Principal Consultant for Cybersecurity at DOT Security, maps where AI already operates inside clinical and administrative workflows, the identity and data exposure paths it opens, and where your SOC needs visibility to minimize overall risk.

Leave with six questions worth putting to your vendors and your own team, and a starting point for governance rather than a new list of fears.

Featured speakers

Meet the speakers

The healthcare, security, and identity leaders joining us to talk SOC operations and AI governance.

Sponsors

Our partners in making this summit possible

Impact Networking logo

Impact Networking

Founded in 1999, Impact Networking is a national managed service provider offering managed IT, cybersecurity, digital transformation, marketing, and print services to businesses of all sizes — today employing more than 900 industry experts across 23 locations nationwide. Impact takes a consultative, long-term approach, partnering with clients to design solutions personal to their business, manage full implementation, and provide ongoing proactive support rather than one-off fixes. For healthcare organizations balancing modernization with day-to-day operational demands, Impact serves as an extended IT and security team.

Linx Security logo

Linx Security

This modern identity governance and access management platform is built for enterprises, giving security teams deep visibility and precise control over who has access to what — across every application, environment, and identity type, human or non-human. Unlike legacy identity systems that are slow to deploy and rigid, Linx is modular and API-first, unifying identity security and access governance so organizations can automate access requests, approvals, and least-privilege enforcement at scale. For healthcare organizations navigating an expanding web of clinical systems, vendors, and AI-driven identities, Linx offers a faster path to closing access gaps and staying audit-ready.

Vega Security logo

Vega Security

We're redefining the boundaries of Cyber Defense by eliminating the limitations of the past. Founded in 2024, Vega is on a mission to help organizations achieve Agentic Cyber Defense by harnessing all their data at AI speed. We do so without the taxes of legacy SIEM that have plagued the industry for 20 years. Backed by Cyberstarts, Accel, Redpoint, and CRV, Vega delivers an Agentic Cyber Defense Platform that transforms every layer of Security Operations. Built on our Security Analytics Mesh, Cyber Defense Engineers can use all their security data, wherever it sits, without migrations or compromises.

Official registration is now open

Register on LinkedIn

Official registration has moved to LinkedIn Events. Click below to reserve your seat and receive updates.

Register on LinkedIn